This landing page contains links to all the University's MFA instructions. You can find more help from this instructions site by using, for example, the search. If you cannot solve the problem with the instructions, don’t hesitate to contact the IT Helpdesk.
Multifactor Authentication (MFA) improves information security by making scam attempts more difficult for cybercriminals. MFA is a feature that provides additional security when logging in to many of the University's services, and it uses a separate device to authenticate.
Authentication methods
The longest login interval for personal devices is 30 days, but some user groups have shorter times, such as the staff: five (5) days. On a risk basis, you may be asked to log in more frequently.
Resetting the authentication methods
If the MFA authentication fails for some reason, you can reset the authentication methods in the MyAccount service at https://myaccount.helsinki.fi.
Note! Resetting MFA authentication methods requires strong authentication. Log in to MyAccount using one of the following authentication methods:
- Suomi.fi
- eIDAS
- Candour ID
- one-time password.
Do you suspect that someone is misusing your username?
If you see an authentication or attempted authentication on the list that you did not make, please contact IT Helpdesk.
Breakage or loss of phone
If your phone breaks or is lost, you can try adding a new device on, for example, your work computer at: https://mysignins.microsoft.com/security-info.
- If you cannot add a new device, you must reset your MFA methods using the MyAccount service at https://myaccount.helsinki.fi.
- For more detailed instructions on resetting MFA authentication methods, see the separate instructions.
For security reasons, we recommend adding MFA authentication to two separate devices.
Additional authentication when logging in
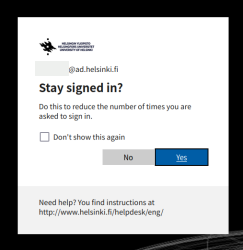
Due to changes to multi-factor authentication (MFA), you may receive an additional message Stay signed in?, when logging in.
You can check the box Don’t show this again and reply Yes.
Problems?
More detailed instructions
Please also read the following more detailed instructions:
Give feedback
The instructions site of the University of Helsinki's IT Helpdesk helps you with IT-related issues related to your work. Let us know how we can improve our instructions. We greatly appreciate your feedback!
How would you improve these instructions?